
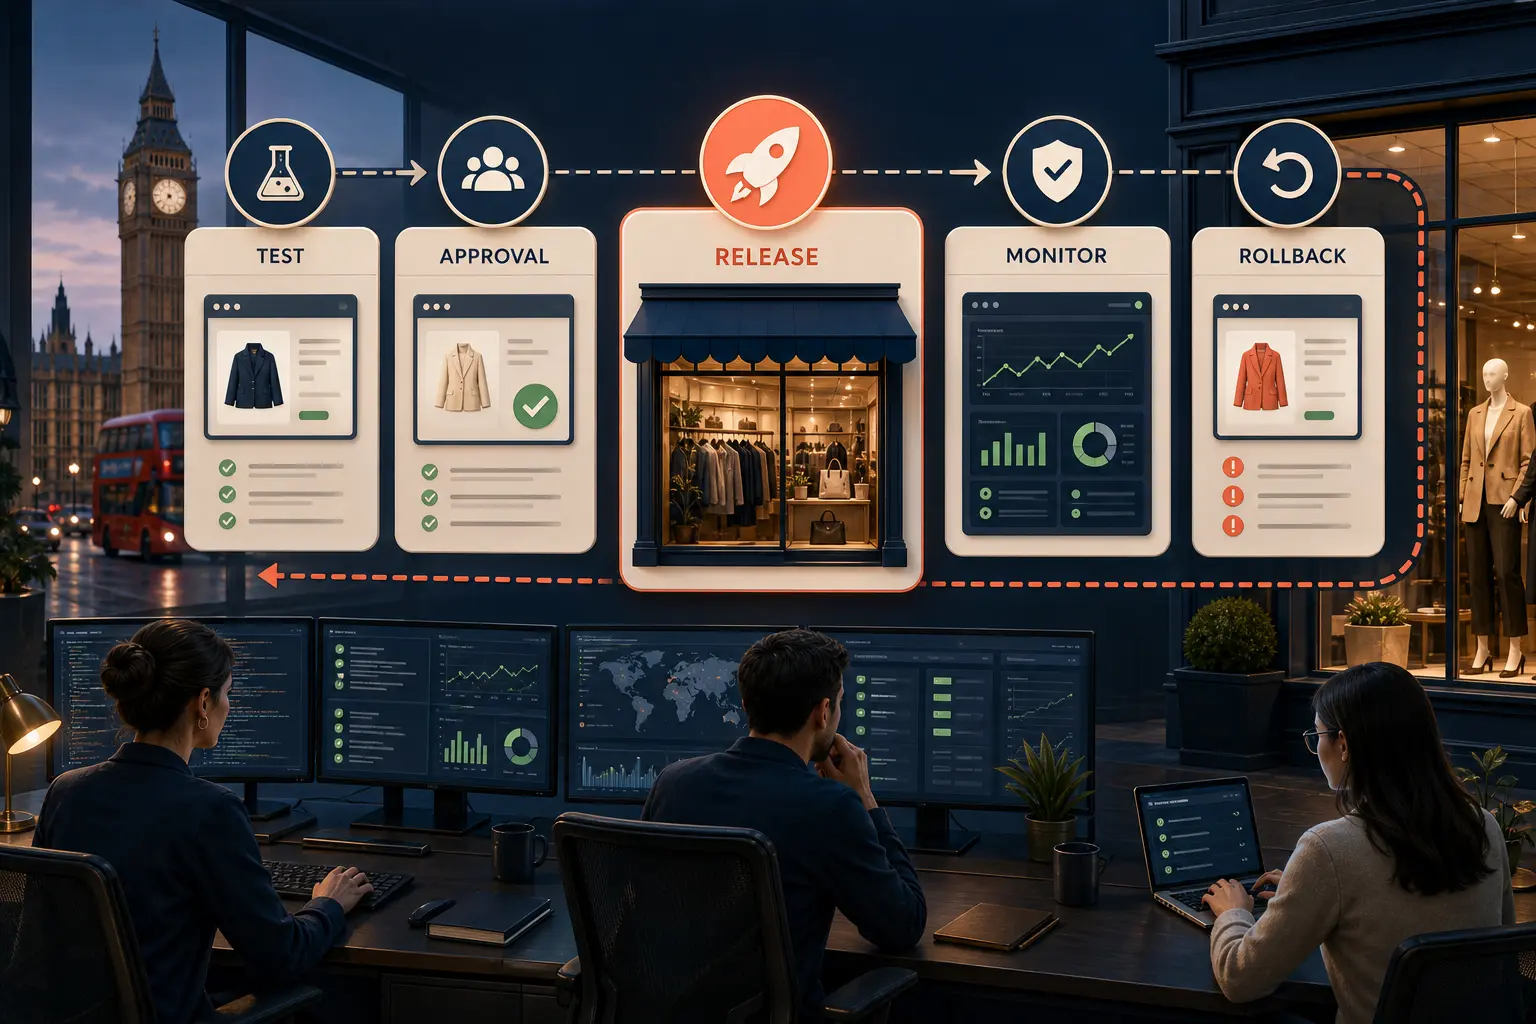
What we have seen is this: Shopify changes become risky when “publish” is treated as the final step. A theme may pass visual review while a discount, app embed, analytics event or warehouse handoff fails. The team then debates whether to wait, patch forward or restore the previous state while live orders continue.
A release and rollback plan makes that decision before pressure arrives. It is proportionate change management for a revenue system, not enterprise theatre.
Table of contents
- Keyword decision
- Define the release unit
- Set acceptance gates
- Prepare rollback by layer
- Monitor the release
- Close the change
- StoreBuilt point of view
Keyword decision
| Decision | Direction |
|---|---|
| Primary keyword | Shopify release plan |
| Secondary keywords | Shopify rollback plan, ecommerce deployment checklist, Shopify change management UK |
| Search intent | Reduce production release risk |
| Funnel stage | Solution and partner evaluation |
| Page type | Operational runbook |
| Why StoreBuilt can win | The guidance joins theme delivery to trading and fulfilment reality |
Competitor articles often cover launch checklists or support retainers. The specific gap is routine release control after launch, when small changes can still affect live revenue.
Define the release unit
List every item moving together: theme version, app embed, metafield definition, navigation, market setting, discount, pixel, webhook or external configuration. Record dependencies and the reason they cannot be separated. Smaller release units are easier to understand and reverse.
| Layer | Example change | Rollback consideration |
|---|---|---|
| Theme | section or template | Republish known-safe theme |
| Content/data | metafield or navigation | Preserve previous values or export |
| App | embed, script or configuration | Disable safely; check data side effects |
| Integration | webhook or mapping | Restore version and reconcile messages |
| Commercial | price or discount | Confirm orders placed during the window |
Name one release owner and one business approver. Include support and operations when customer messages or fulfilment behaviour change.
Set acceptance gates
Define expected behaviour before testing. Cover mobile and desktop, representative products, markets, customer states and payment paths. Check accessibility, performance and analytics in proportion to the change. A screenshot proves appearance, not order integrity.
An anonymous StoreBuilt release review found a safe-looking collection update that also altered product-card purchase behaviour through a shared component. Expanding acceptance from the requested page to the reused component’s journeys caught the regression before production.
Do not release with unexplained failed checks. Record an explicit risk acceptance if a non-critical defect is deferred, with an owner and deadline.
Prepare rollback by layer
Keep a named, known-safe theme available. Export or record settings and content that will be modified. Document how to reverse app configuration and integration versions. Confirm who has permissions to perform each action.
Rollback does not undo history. Orders, payments, customer submissions and webhook messages created during the release window still need reconciliation. If a data migration is destructive or difficult to reverse, use a staged approach and backup rather than pretending theme rollback is enough.
Agree triggers before launch: checkout failure, wrong pricing, widespread JavaScript error, broken order export or a severe performance change. Add a time boundary for investigation so the team does not leave customers exposed while debating a fix.
Monitor the release
Run smoke tests immediately after publication. Watch checkout and payment success, error monitoring, analytics continuity, site search, customer contacts and the exact metric the change intended to improve. Compare by device and market where relevant.
Use one incident channel and timeline. Freeze unrelated changes during the observation window. If a trigger is met, the release owner executes the documented rollback and announces the state; they do not wait for a large committee to rediscover the decision.
A Shopify support and maintenance retainer should provide this ownership, while Shopify development should leave behind a maintainable release path.
Close the change
Confirm that temporary flags, duplicated themes and test data are cleaned up. Record actual results, customer issues and any manual reconciliation. Update the runbook when the release exposed a missing dependency or permission.
Contact StoreBuilt if Shopify releases depend on memory and hope rather than evidence.
+## Introduce the process in four releases
Use the next four changes to build the habit. For release one, record scope, owner, approver and smoke tests. For release two, identify a safe theme or configuration and rehearse reversal away from peak trading. For release three, define monitoring and rollback triggers. For release four, run a retrospective and update the template.
Scale the process with risk. A copy correction may need peer review and a rendered-page check. Checkout, subscription, pricing or ERP changes need representative orders, reconciliation and cross-team approval. Classify risk by revenue surface, reversibility, data mutation, customer reach and dependency count.
Maintain a release calendar visible to trading, support and fulfilment. Avoid stacking unrelated changes before campaigns. Measure escaped defects, detection time, rollback time, affected orders and repeated failure types. The objective is a shorter path from a detected problem to a safe response while useful improvements continue to reach customers.
+## Decide between rollback and fixing forward
Rollback is appropriate when the previous state is known-safe, the fault is severe and reversal is less risky than diagnosis in production. Fixing forward may be better when orders or data have already moved to a new structure, the defect is isolated and a tested correction is genuinely faster. Make the choice against written criteria, not pride in the release.
If rollback occurs, preserve logs and evidence first when doing so will not prolong customer harm. Announce what changed to support and operations, then reconcile orders and messages created during the affected period. Do not label the event resolved merely because the old theme is live.
A blameless review should ask why the acceptance gate missed the problem, why monitoring did or did not detect it, and whether the recovery instructions were accurate. Convert answers into one or two owned improvements. Large retrospective documents without assigned changes provide very little protection for the next release.
Keep emergency access current and protected. At least two authorised people should be able to publish the safe theme or reverse the relevant configuration, with strong authentication and an auditable handover. Test access before high-risk releases; discovering an expired account during an incident turns a technical fault into an avoidable operational delay.
For multilingual releases, include translation quality assurance so source changes do not leave older promises visible in another language.
StoreBuilt point of view
StoreBuilt believes every production change should be observable and reversible in proportion to its risk. The goal is not zero change; it is confident delivery with a clear decision when reality differs from the plan.
Contact StoreBuilt to establish a safer Shopify release workflow.